PhishStick Blocked Phishing Email Highlight - October 2026
For the month of September, PhishStick successfully blocked 15,369 attacks, which is an average of 495 attacks per day. The most common attack type remains Phishing: Credential.
If you received any of potential Phishing or Spam email, please forward the email to Phishing@rpi.edu, or report through the Report Message button in Outlook.
Trending Attack - Credential Phishing with Name Impersonation
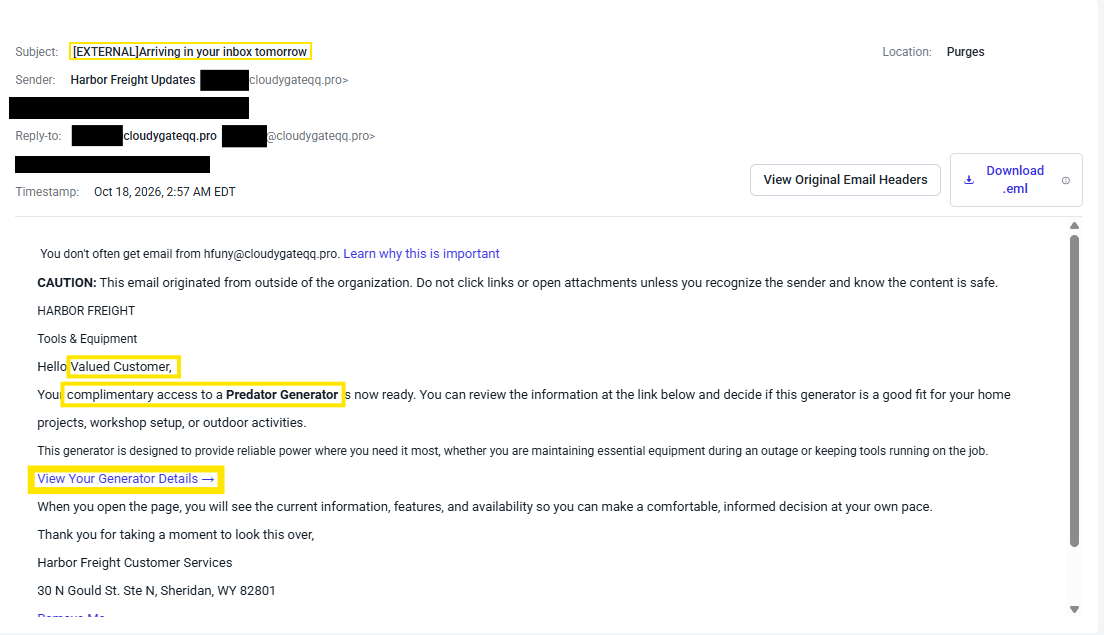
The email below, subject-lined "[EXTERNAL]Arriving in your inbox tomorrow," was attempted to be sent by bad actors to multiple RPI mailboxes, however, was blocked by PhishStick before reaching Student, Faculty, and Staff Inboxes.
While the display name of this email shows "Harbor Freight Updates," the sender address and domain are malicious, and exhibit several Phishing red flags attempting to capture RCS credentials. Please see analysis provided below:
Key Security Signals:
- Sender Impersonation - This bad actor impersonated the company "Harbor Freight," as the display name of the email shows SharePoint, however, the Reply-to: and CC: of the email are to a malicious sender domain attempting to Phish RCS Account credentials.
- [External] Flag/Sense of Urgency - Further scrutiny for any emails with the [External] tag, especially if this is for an unexpected shipment or package. This email's subject also includes a sense of urgency of this is "Arriving in your Inbox tomorrow," prompting recipients to act quickly.
- Malicious URLs - Hover/Don't Click! - The URLs in this email direct to a malicious webpage to steal credentials. Mouse over any URL links in the body of an email, and if you do not recognize the URL, or if the URL is using a shortener service such as Tiny URL, do not click the link!
- Mass-Sent Phish - This email was sent to several RPI Community recipients with the same email content. This is a tactic called bulk-phishing, where bad actors send identical emails to as many mailboxes at once, hoping a small fraction of recipients will fall for the Phish.
- Generic Greeting - This email includes a generic greeting, and is not addressed to a specific Client. Extra caution should be utilized for any email that does not have a personal greeting or signature.
- Too good to be true - This email maliciously advertises "complimentary access" to a Predator Generator, which is a too good to be true offer for an expensive whole house or workshop generator system.
What to do?